

Overview
Network Access Control (NAC) is the part of Taranac that decides who and what is allowed onto your network and with which access. When a laptop, phone, printer, or camera connects to a switch port or wireless SSID, the switch (the authenticator) asks Taranac over RADIUS whether to admit the device and on what terms — which VLAN, which ACL, for how long. This is the same role Cisco ISE plays: 802.1X / MAB access control with endpoint classification and an authorization policy.
NAC runs alongside Taranac’s device-admin AAA but is a separate subsystem with its own RADIUS service, its own policy engine, and its own admin pages. Everything below describes how you configure and reason about it in the Taranac admin UI.
- 1 Authenticate MAB · MAC identity
- 2 Classify group: Printers
- 3 Authorize first match wins
- 4 Result VLAN 30 · ACL
- 5 CoA change live session
NAC vs. device-admin AAA
Section titled “NAC vs. device-admin AAA”Taranac does two different jobs that both speak RADIUS, and it is easy to confuse them. AAA controls administrators logging into network gear (TACACS+ / RADIUS device administration). NAC controls endpoints getting onto the network (802.1X / MAB). They share the database and the admin UI but nothing else — separate RADIUS containers, separate ports, separate policies.
| Aspect | Device-admin AAA | NAC |
|---|---|---|
| Goal | Access to a device’s CLI/management | Access to a network port or SSID |
| Protocol | TACACS+ and RADIUS | RADIUS only (802.1X, MAB) |
| Who/what authenticates | An administrator (username/password) | An endpoint or its user (EAP, certificate, MAC) |
| Result | Shell, privilege level, allowed commands | VLAN, ACL, session timeout, redirect |
| Engine | AAA policy rules | NAC policy rules |
The access flow
Section titled “The access flow”Every NAC decision follows the same pipeline. Understanding it makes the rest of the configuration obvious:
- Authenticate — the endpoint proves identity. With 802.1X a supplicant runs EAP (PEAP, EAP-TLS, or EAP-TTLS). If there is no supplicant, the switch falls back to MAB (MAC Authentication Bypass), where the MAC address itself is the identity.
- Classify the endpoint — Taranac looks up (or auto-discovers) the endpoint by MAC, enriches it with vendor (from the IEEE OUI database) and certificate/hostname data, and assigns it to one or more endpoint groups via classification rules. Classification re-runs on every authentication.
- Authorization policy — the NAC policy engine evaluates ordered rules (first match wins) against the request: the authentication method, the user’s groups, the endpoint’s groups, the NAS device’s groups, and the time of day.
- Result — the matched rule yields either Reject or an authorization profile (VLAN, ACL, session timeout, optional web redirect). Taranac renders that intent into the correct vendor-specific RADIUS attributes and returns Access-Accept.
- CoA (Change of Authorization) — after the session is live, an admin can push a change — re-authenticate, bounce the port, change VLAN, or disconnect — without the endpoint reconnecting on its own.
Building blocks
Section titled “Building blocks”Each concept below maps to a page in the NAC section of the admin UI.
| Building block | What it is | Where in the UI |
|---|---|---|
| Endpoints | The inventory of devices, keyed by MAC. Each has a status, a persistence type, vendor, and group memberships. | Endpoints |
| Endpoint groups | Categories used in policy (Printers, Corporate Devices, Guest…). Membership is automatic via classification rules or manual. | Endpoints → Endpoint Groups |
| Authentication methods | How an endpoint proves identity: PEAP, EAP-TLS, EAP-TTLS (802.1X) or MAB. | (configured per policy rule) |
| Authorization profiles | Vendor-agnostic intent: VLAN, ACL, session timeout, redirect. | Policies → Authorization Profiles |
| NAC policy | The ordered rule table that maps requests to a profile or Reject. | Policies → Policy Table |
| Sessions | Live 802.1X / MAB sessions — what CoA acts on, aged out by their own accounting stream. | Logging & Reports → NAC Logs → Sessions |
| Captive portal | Guest / BYOD / self-registration / AUP web flows for unknown devices. | Endpoints → Captive Portals |
| PKI & trust | Server certificate for EAP, internal CA, trusted CAs for client certificates. | Settings → PKI / Certificates |
Endpoints
Section titled “Endpoints”An endpoint is a network device identified by its MAC address. It can be added manually, imported from CSV, synced from a directory’s computer objects (Active Directory, FreeIPA, OpenLDAP or generic LDAP), or auto-discovered the first time it authenticates. Each endpoint carries:
- a status:
known,unknown,blocked, orinactive; - a persistence type:
static(manual/LDAP/pinned — never auto-removed),dynamic(discovered via RADIUS — subject to lifecycle cleanup), orguest(created by the captive portal — removed after inactivity); - enrichment data: vendor (resolved from the OUI prefix), hostname, IP, and certificate identity when EAP-TLS is used.
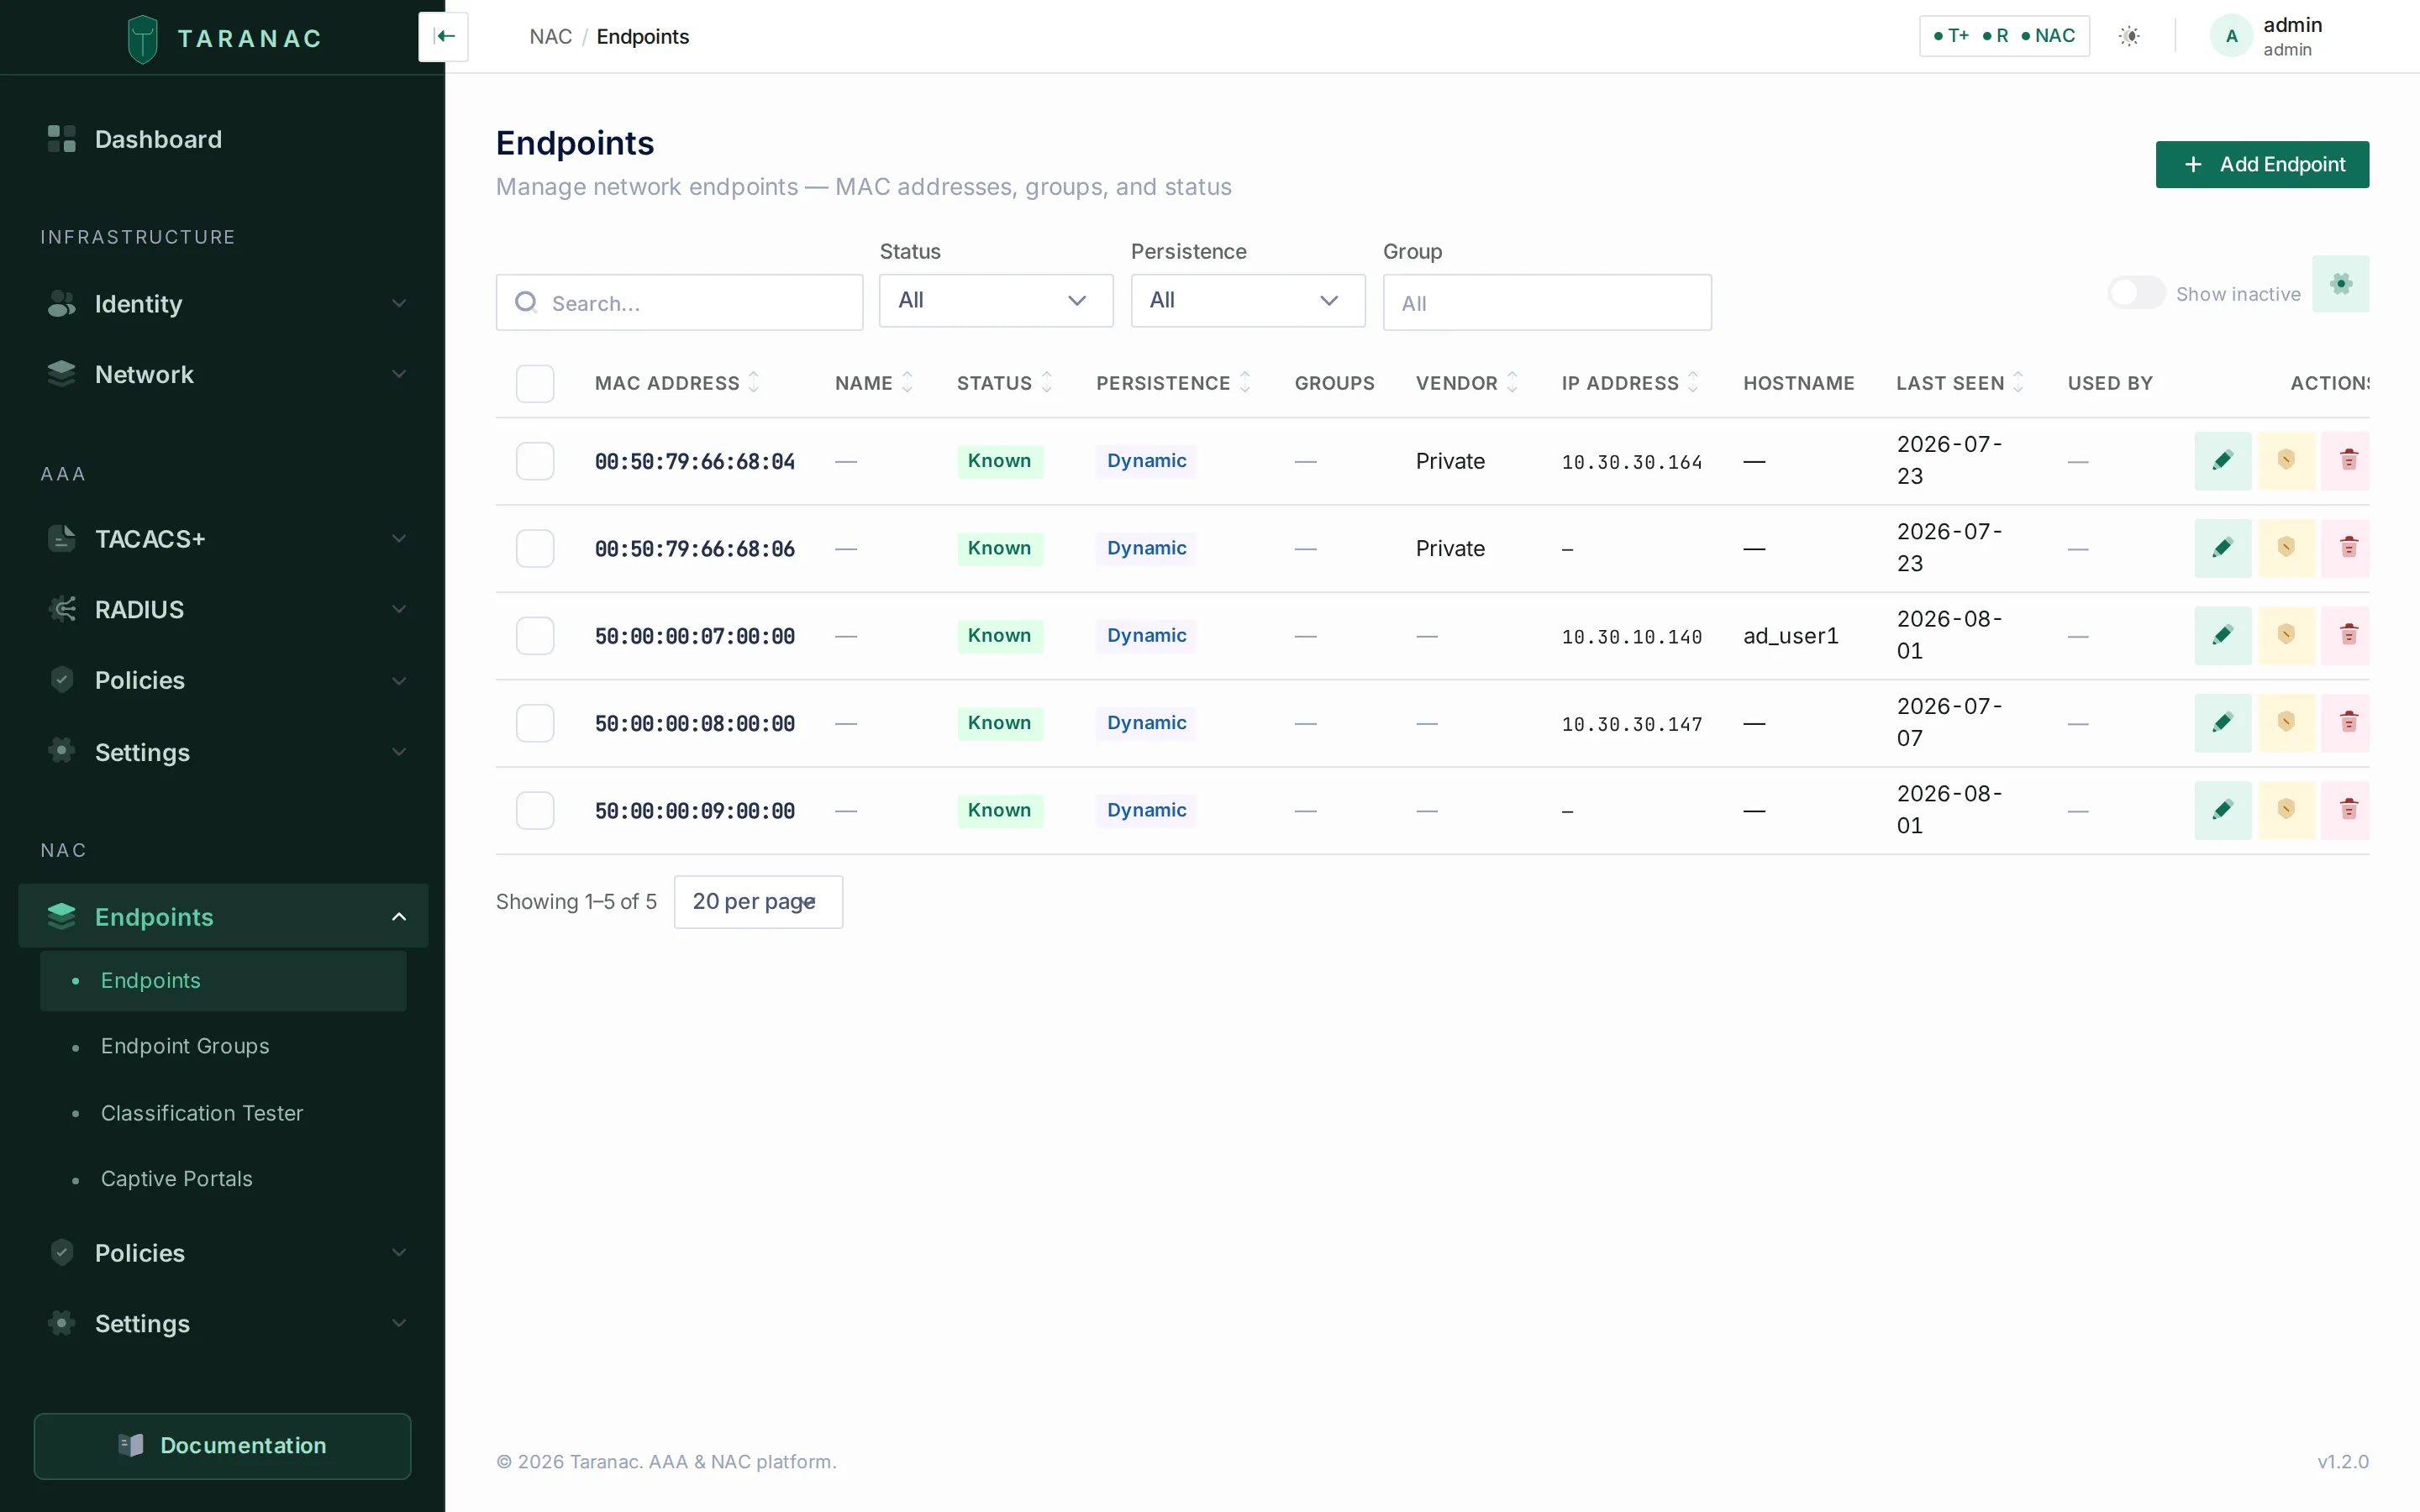 The Endpoints page: every device by MAC, with status, persistence, group membership, and vendor.
Endpoint groups and classification
Section titled “Endpoint groups and classification”Groups are how endpoints enter the policy. Rather than listing MACs in rules, you put devices into groups and write rules about groups. A group can have classification rules that assign endpoints automatically. Matching is all-matches — every enabled rule whose condition fires adds the endpoint to its group, so a device can belong to several groups at once. Devices that match nothing land in “Unclassified”.
| Match type | Matches on |
|---|---|
exact_mac | A specific full MAC address |
oui_prefix | The first three bytes (one vendor’s whole address block) |
mac_pattern | A substring of the MAC string |
vendor_name | The OUI vendor name (case-insensitive substring) |
cert_issuer | The issuing CA of the endpoint’s certificate |
cert_identity_pattern | CN or DNS SAN from a machine certificate (glob) |
hostname_pattern | The endpoint’s hostname (glob) |
ldap_dn | The directory container the machine’s object sits in, and everything below it |
ldap_group | A directory group the machine belongs to, nested membership included |
The last two read the directory and need computer sync on the connection they name; both arrived in 1.2.7. See directory-based classification.
Authentication methods
Section titled “Authentication methods”| Method | How it works | Typical use |
|---|---|---|
| PEAP (MSCHAPv2) | TLS tunnel, inner username/password against local users or LDAP | Domain users with password-based 802.1X |
| EAP-TLS | Mutual TLS with a client certificate; identity from the cert (UPN/CN/SAN) | Corporate machines and users with certificates |
| EAP-TTLS (PAP) | TLS tunnel, inner PAP verified by LDAP bind | LDAP/AD users on Linux supplicants |
| MAB | No supplicant — the MAC address is the identity | Printers, IP phones, cameras, IoT |
See 802.1X authentication for supplicant configuration and the full EAP details.
Authorization profiles and policy
Section titled “Authorization profiles and policy”An authorization profile describes what the network should do in vendor-neutral terms — assign VLAN 100, apply ACL PRINTERS-ONLY, set a session timeout — without knowing which vendor’s switch is involved. At runtime the Vendor Dictionary translates that intent into the right RADIUS attributes for the actual NAS — Cisco IOS/IOS-XE and NX-OS, Arista EOS, Juniper, Huawei VRP, H3C/Comware, Aruba (AOS-CX / Controllers), HPE ProCurve/ArubaOS-Switch, Fortinet, Dell, Extreme EXOS, Ruckus ICX, MikroTik RouterOS and more, plus a generic RFC-standard entry for anything else. One profile therefore works across a mixed-vendor estate.
The NAC policy is a single flat, ordered rule list — first match wins. Each rule combines up to five conditions (all dimensions ANDed; values within a dimension ORed):
- HOW — authentication method (PEAP / EAP-TLS / EAP-TTLS / MAB / Any)
- WHO — user groups (relevant for 802.1X)
- WHAT — endpoint groups
- WHERE — NAS device groups
- WHEN — always, or a time range
A rule’s action is either Permit (with an authorization profile) or Reject. The default catch-all rule rejects anything unmatched.
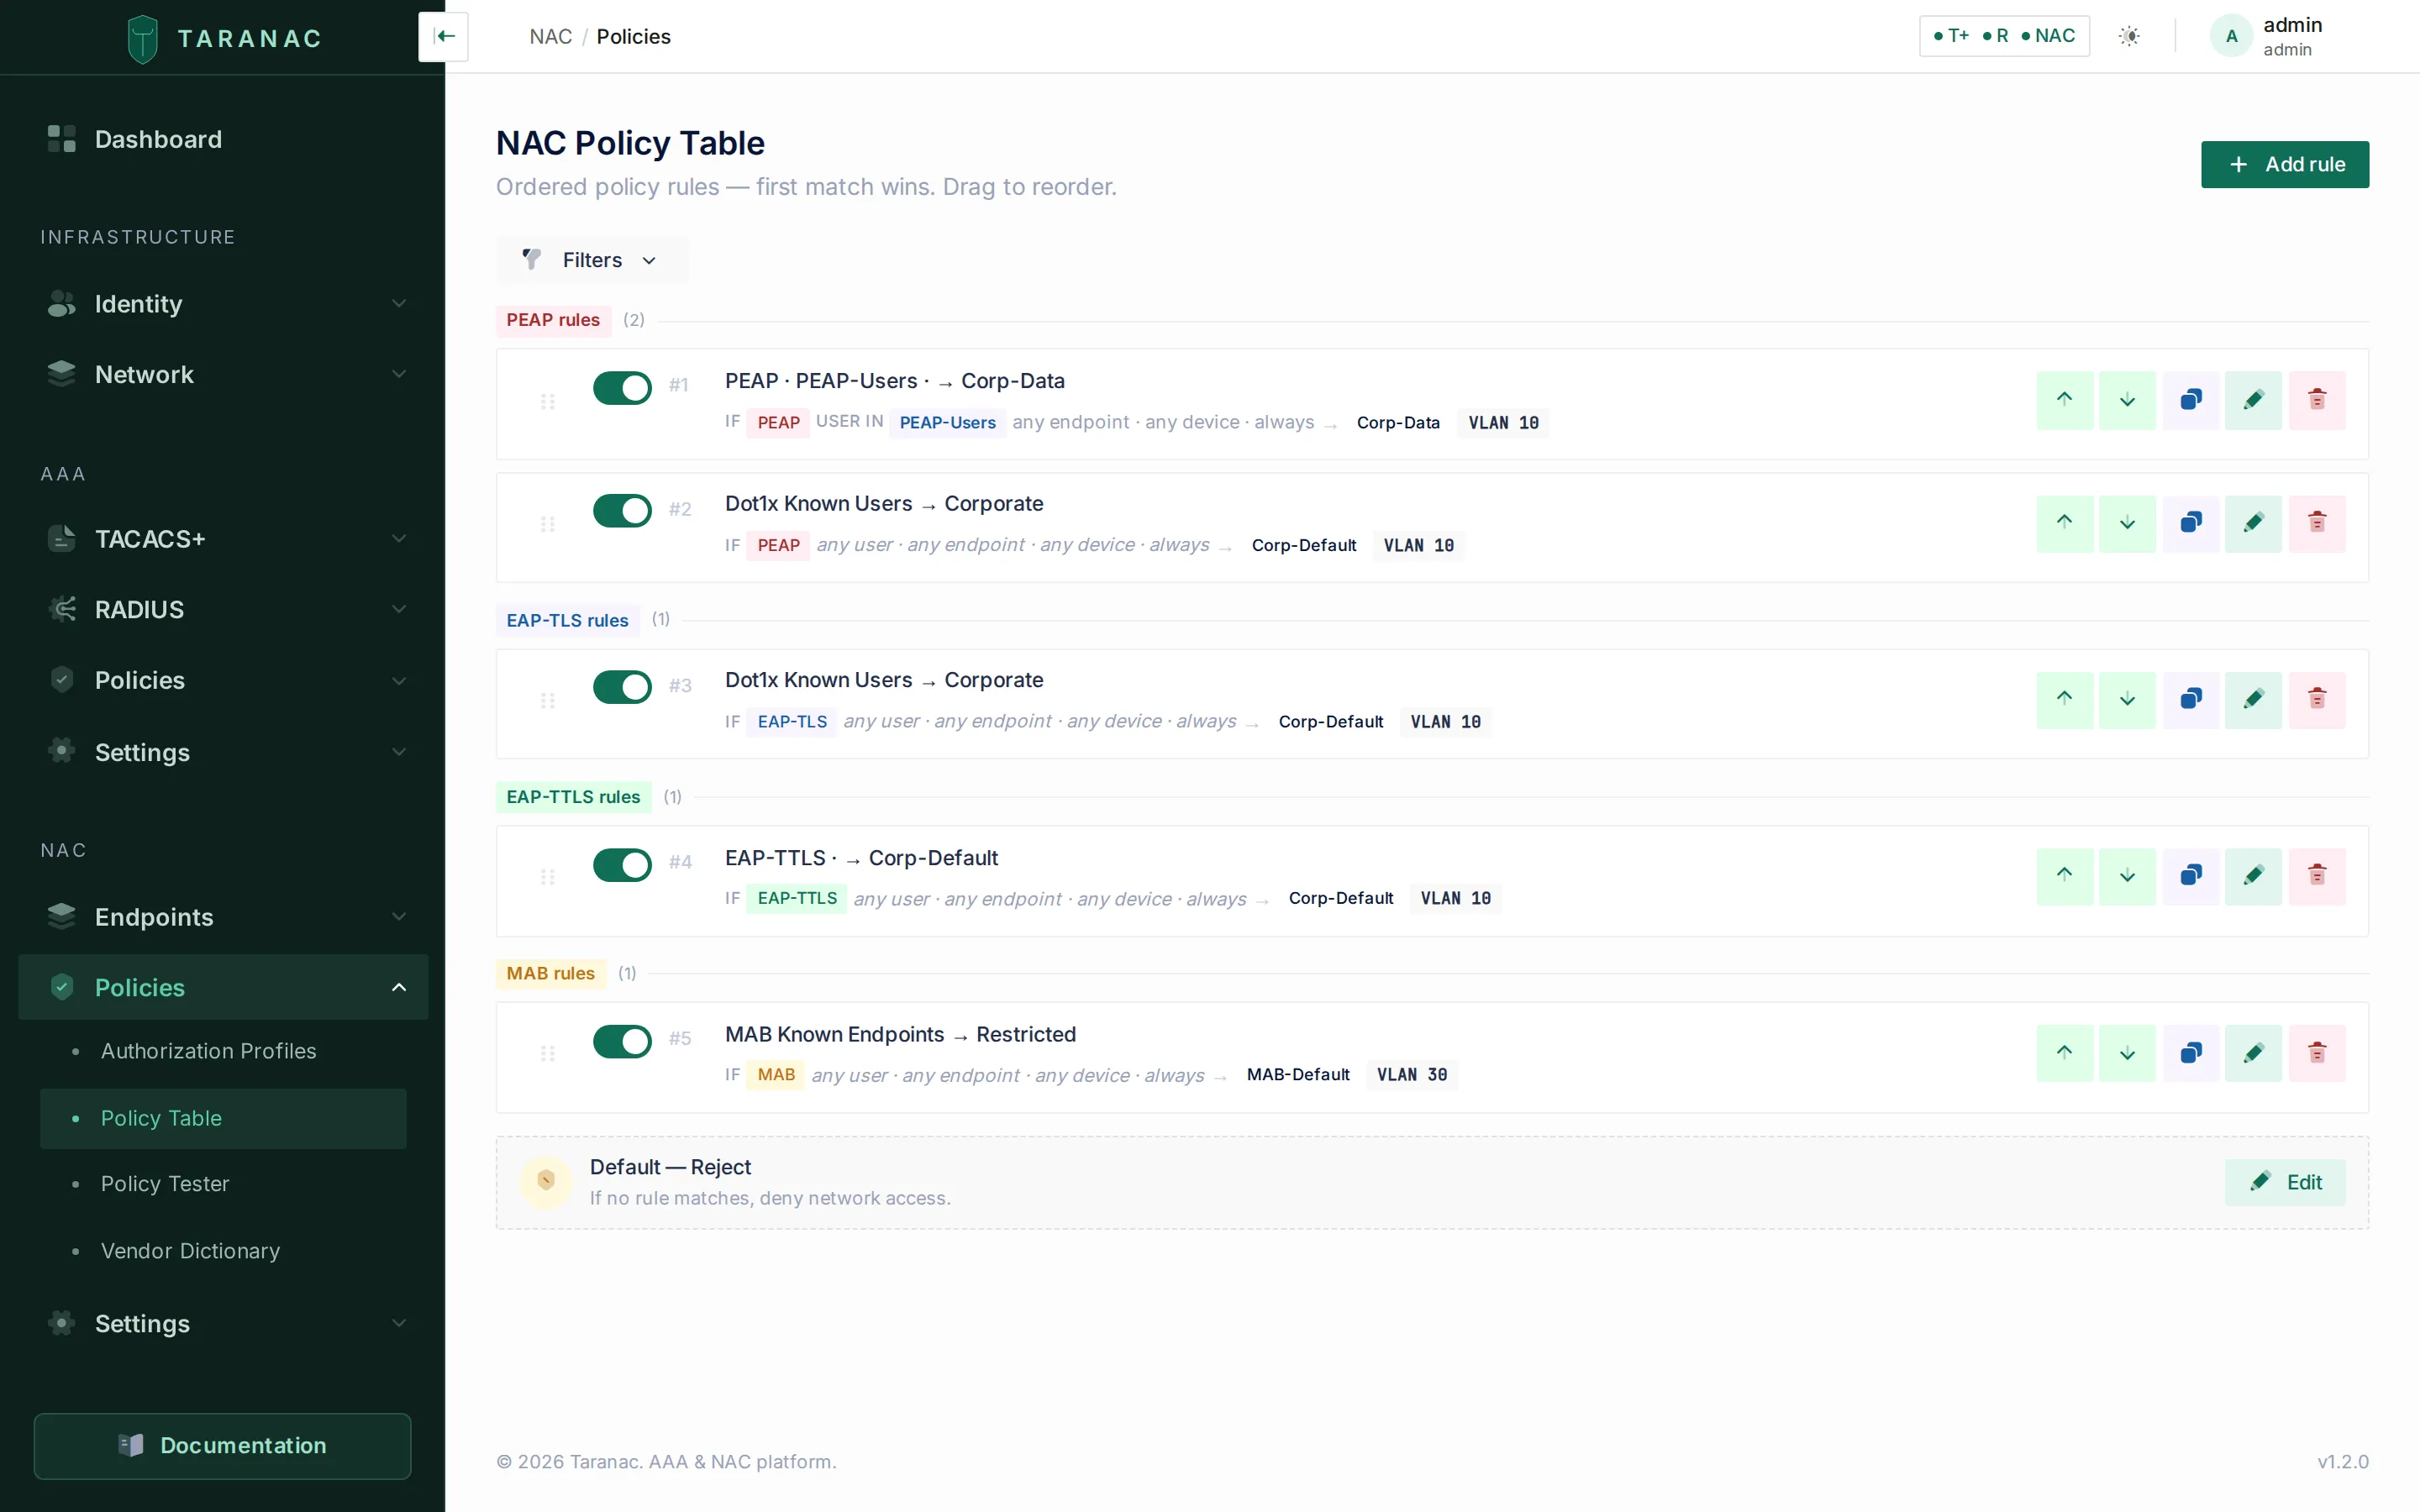 The NAC policy table: ordered rules grouped by authentication method, each rendered as a readable sentence ending in a profile or Reject.
Sessions
Section titled “Sessions”A permitted authentication becomes a session — one endpoint, live on one port — listed under Logging & Reports → NAC Logs → Sessions. That page is the surface CoA acts on, and a session records the VLAN Taranac assigned and the VLAN the switch reported as two separate values; a disagreement between them is flagged, because that is where the port actually settled after authorization.
Taranac learns that a session is over from its accounting stream, and never by asking the switch. There is no way to ask: RFC 5176 defines no read-only packet, and the identification-only CoA-Request once used as one is answered CoA-ACK while removing the RADIUS-assigned VLAN from a live session on any NAS with replace semantics — measured on Huawei VRP, where the user stays authenticated and drops to the port PVID. Nothing in Taranac now closes a session on the strength of a NAS’s answer, so silence is read in two windows:
- a session whose switch does send Accounting Interim-Updates ends after silence past the stale threshold (
nac.session_stale_threshold_minutes, 1440 minutes — 24 hours — by default); - a session where only the Accounting-Start ever arrived cannot be judged by silence at all — on a switch without periodic interim accounting that is the normal state of a perfectly healthy session — so it is held by age alone: Max Session Duration on Settings → NAC, 120 hours by default. Archiving one is logged as a warning naming the cure, which is enabling periodic interim accounting on that switch.
Captive portal and PKI
Section titled “Captive portal and PKI”For devices that have no supplicant and no known MAC, a policy rule can redirect them to a captive portal for guest access, BYOD onboarding, employee self-registration, or acceptance-of-use. Once they register, Taranac issues a CoA to move them into the right VLAN. A portal runs either embedded in the Taranac stack or standalone in a branch DMZ, where it can serve its own DHCP and DNS and proxy registration back to the core. See Captive portal.
EAP needs certificates. Taranac includes an internal PKI: a server certificate that FreeRADIUS presents during every EAP handshake, an internal CA hierarchy to issue user/device certificates, trusted CAs to validate client certificates from outside domains, plus CRL-based revocation and EST enrollment. See PKI & trust.
Common scenarios
Section titled “Common scenarios”| Scenario | Method | Outcome |
|---|---|---|
| Corporate laptop, domain user | PEAP or EAP-TLS → WHO=corporate group | Permit → corporate VLAN, full access |
| Domain machine, no logged-in user | EAP-TLS (machine cert) → WHAT=corporate computers | Permit → machine VLAN |
| Contractor’s own laptop | EAP-TLS against a Trusted CA → WHO=contractors | Permit → restricted VLAN |
| Printer / IP phone / camera | MAB → WHAT=Printers / IP Phones | Permit → device VLAN with restrictive ACL |
| Unknown device | MAB miss → no match | Reject, or redirect to captive portal |
When to use what
Section titled “When to use what”| If you want to… | Use |
|---|---|
| Authenticate users with AD passwords | PEAP (local NT-hash) or EAP-TTLS (LDAP bind) |
| Authenticate by certificate (strongest) | EAP-TLS with the internal PKI or a Trusted CA |
| Admit devices that cannot run a supplicant | MAB plus a tight endpoint group + ACL profile |
| Onboard guests / personal devices | A captive portal flow + redirect profile |
| Apply one policy across mixed switch vendors | Vendor-agnostic authorization profiles + Vendor Dictionary |
| Move a live device to a new VLAN immediately | CoA from the endpoint’s quick actions, or from Logging & Reports → NAC Logs → Sessions |
Related
Section titled “Related”- Endpoints — inventory, classification, lifecycle
- 802.1X authentication — PEAP, EAP-TLS, EAP-TTLS, MAB
- NAC policy — authorization profiles, rules, the Vendor Dictionary
- Captive portal — guest, BYOD, self-registration, AUP
- PKI & trust — server cert, internal CA, trusted CAs
- Taranac on GitHub